Field notes on governing agents. Written while we build the authority layer.
Essays on running AI agents inside your rules: runtime security, the EU AI Act, MCP, agent identity, and the record your auditor will ask for.
✓29 posts · newest September 30, 2026
 Latest
Europe Just Published Its First AI Quality Standard. Here's the Part It Can't Enforce.
EN 18286 turns Article 17’s quality-management obligation into an auditable framework. A management system proves you designed the right process. It cannot prove your agents behaved that way at runtime.Read the postAll posts
Every field note. Newest first.
Europe Just Published Its First AI Quality Standard. Here's the Part It Can't Enforce.
EN 18286 turns Article 17’s quality-management obligation into an auditable framework. A management system proves you designed the right process. It cannot prove your agents behaved that way at runtime.
The 72-Hour Clock, for an AI Incident
Article 33 starts counting from awareness, not from certainty. What you need at hour one when the subject is an agent, and why debugging telemetry cannot answer it.
Agents on the Plant Floor
OT governance is not IT governance with different nouns. Rollback does not exist, the safety case is a legal artefact with decades of precedent, and latency is a correctness property.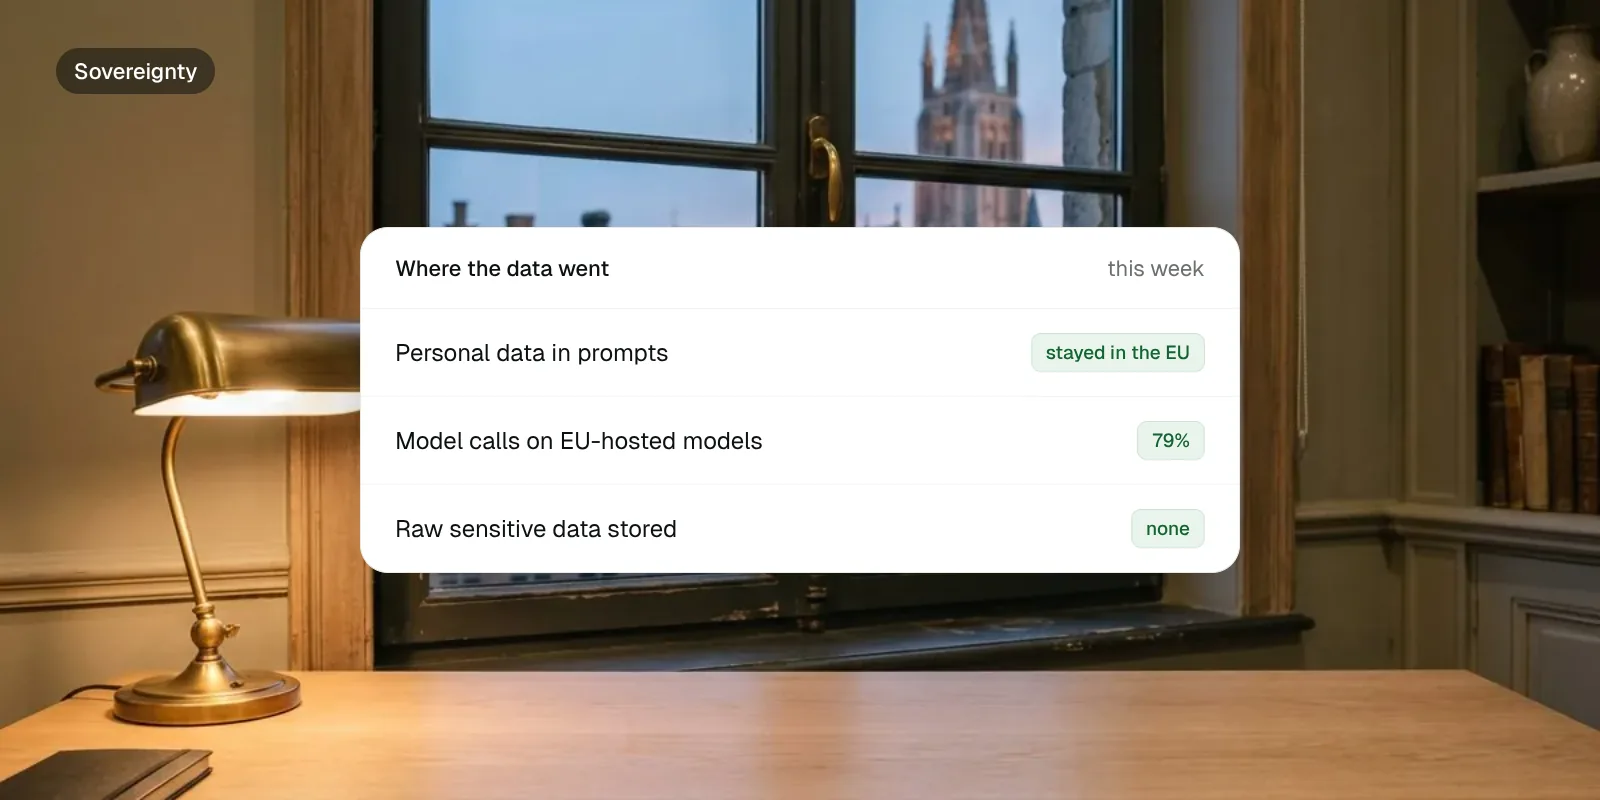
Where Your Agent’s Data Actually Goes
“EU-only” is a claim about one hop. A single agent request makes six. The map, hop by hop, and the two that leak most often.
What the MCP Boundary Actually Exposes
An MCP server is a privilege boundary and the ecosystem treats it like a plugin directory. Three things cross it, not one, and each is a different risk.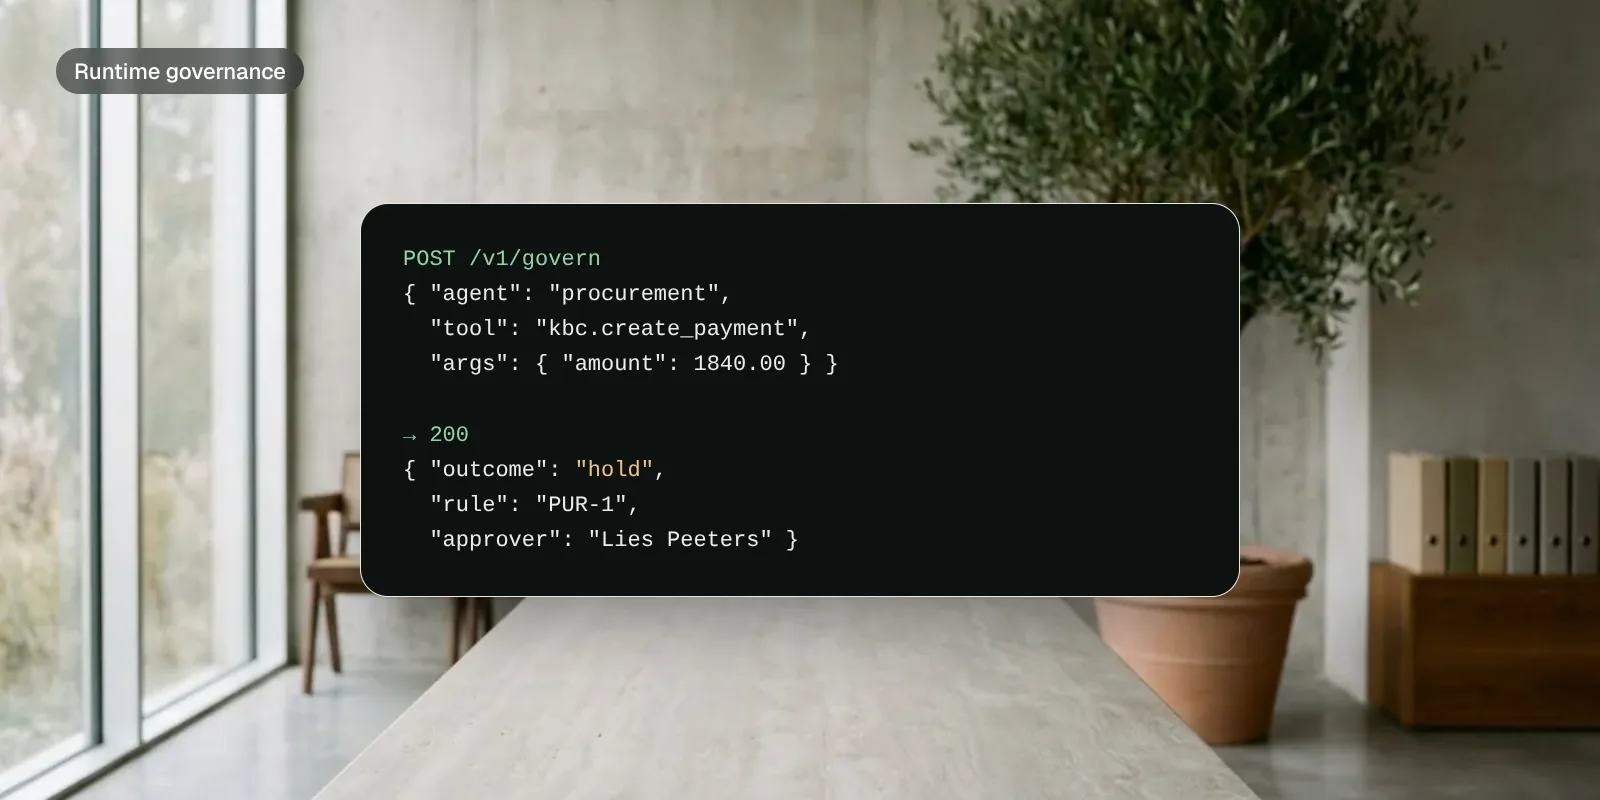
Runtime Is Where Agent Security Gets Real
A valid credential doesn’t make a live action valid. Runtime governance enforces agent actions inline, before they complete, and it’s becoming its own security category.
Give Your Agents Less. On Purpose.
Everyone is racing to give AI agents more power. The hard problem is giving them less. Precisely less. Least privilege for capabilities and instructions, plus progressive authority.
AI-Powered Cybersecurity Meets AI Governance
AI is transforming cybersecurity. But who secures the AI doing the securing? When your security tools are autonomous agents, they need governance too.
Securing AI Agents in Regulated Industries
When a bad AI decision has a dollar figure, a patient outcome, or a legal liability attached, security is not optional.
Real-Time Monitoring for AI Agents: Beyond Dashboards
Dashboards were built for human-speed decisions. When AI agents process 200 cases per hour, you need monitoring that can keep up.
AI Security in 2026: What CISOs Actually Need
The AI security landscape shifted from model safety to agent governance. Here is what matters now.
The IETF Just Published an AI Agent Auth Framework. Here's What It Gets Right.
draft-klrc-aiagent-auth-00 proposes SPIFFE, OAuth 2.0, and WIMSE for agent identity. A technical reading of what it means and what it misses.
An AI Agent Risk Assessment Framework for Security Teams
Five risk categories, weighted scoring, and go/no-go criteria. A practical framework for evaluating AI agents before production deployment.
Cloud Security's Lessons for AI Governance: What We Already Learned Once
Every AI governance mistake was already made with cloud. Shadow IT, shared credentials, missing audit trails. The playbook exists.
The CISO AI Readiness Score: A Self-Assessment Framework
8 dimensions, scored 0-4. A practical framework to measure where your organization stands on AI agent governance.
EU AI Act Compliance: What You Should Be Doing Right Now
Enforcement starts August 2026. Here is what to do before the deadline.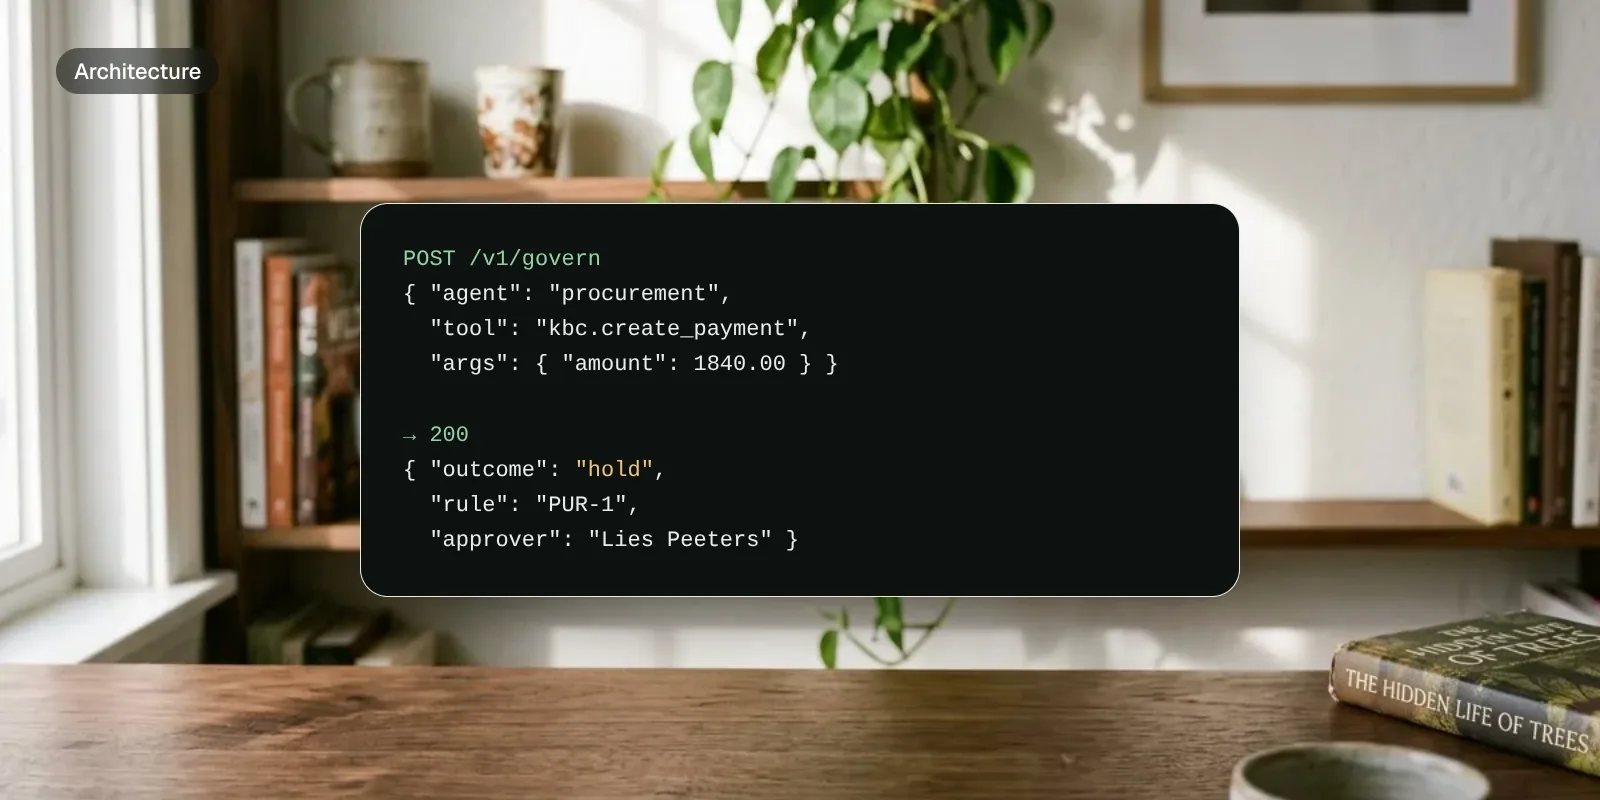
Designing Auditable AI Agents from Day One
Most teams retrofit auditability. Here are five design principles for agents that generate compliance evidence as a byproduct.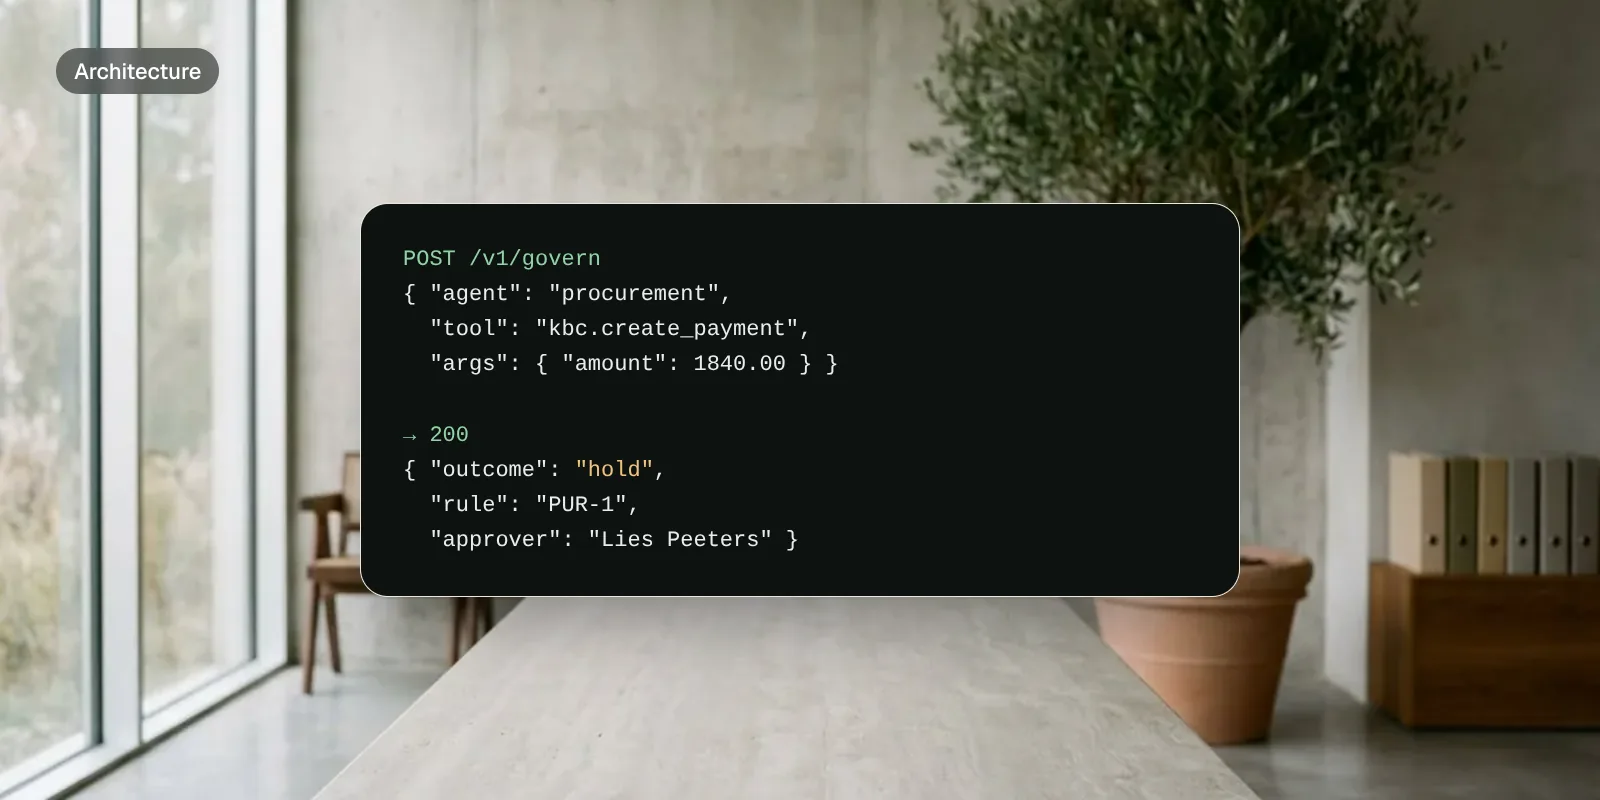
Why Your AI Agent Needs an Identity, Not Just an API Key
Shared API keys mean you can't tell agents apart. Here is what real agent identity looks like.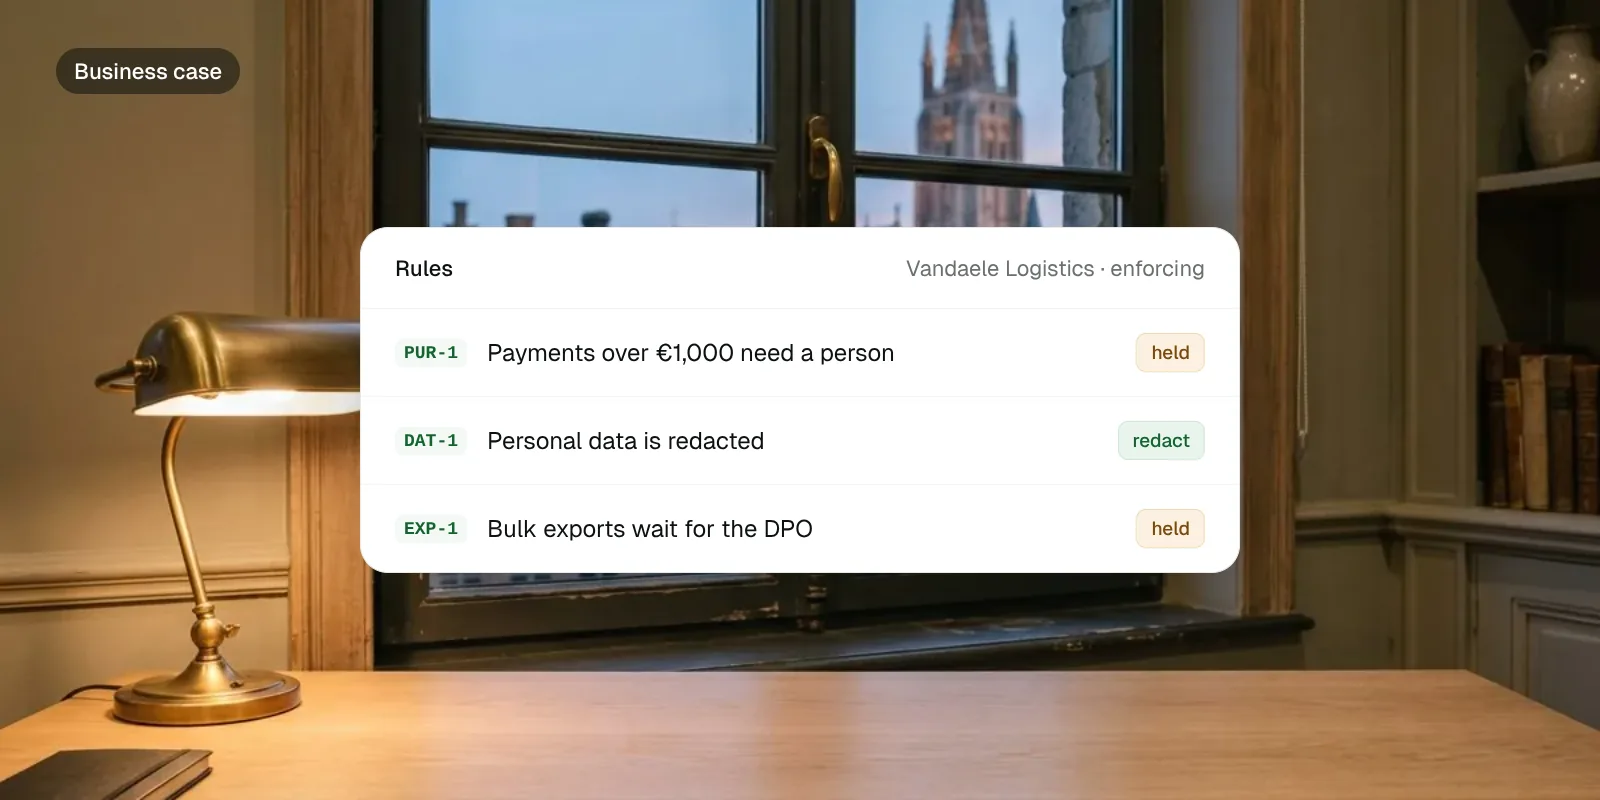
The Cost of Waiting: What Happens When AI Governance Comes After the Incident
Three scenarios. Three cost calculations. The math is clearer than you think.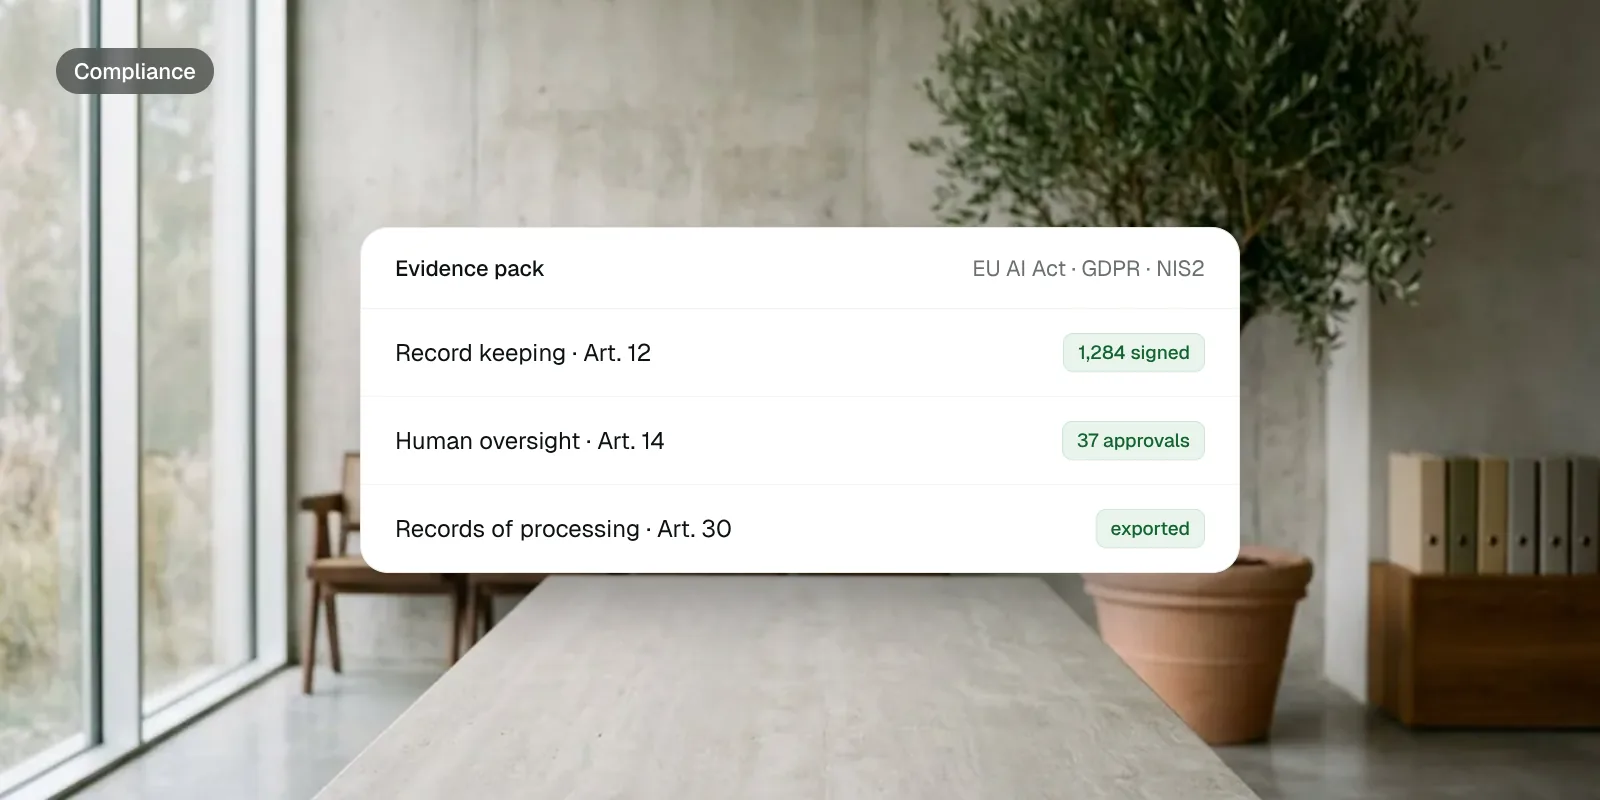
DORA and AI: What Financial Services Need to Know
DORA treats AI agents as ICT assets. Operational resilience testing, incident reporting, third-party risk.
Zero Trust for AI Agents: What Least Privilege Actually Means
Least privilege for humans is well understood. For AI agents, it barely exists.
Prompt Injection Is Not an AI Problem. It's an Agent Problem.
The real risk is not making the model say bad things. It's making the agent do bad things.
AI Governance Is Not AI Ethics
Ethics is about what you should build. Governance is about what you can prove you controlled.
Sandboxing AI Agents: Why Isolation Alone Is Not Enough
Kernel sandboxes lock down the process. Policy governs what the agent is allowed to do.
EU AI Act Article 14: What Human Oversight Actually Requires
Everyone knows they need "human oversight." Almost nobody agrees on what that means.
Shadow AI Is a Governance Problem, Not a Security Problem
Your teams are deploying AI agents without telling security. You need a governed path that's faster than going around you.
What Your AI Audit Trail Is Missing
Most teams log prompts and token counts. When the auditor asks what happened, the answer is incomplete.
AI Agent Security Is Not LLM Security
The threat model is fundamentally different from securing a language model.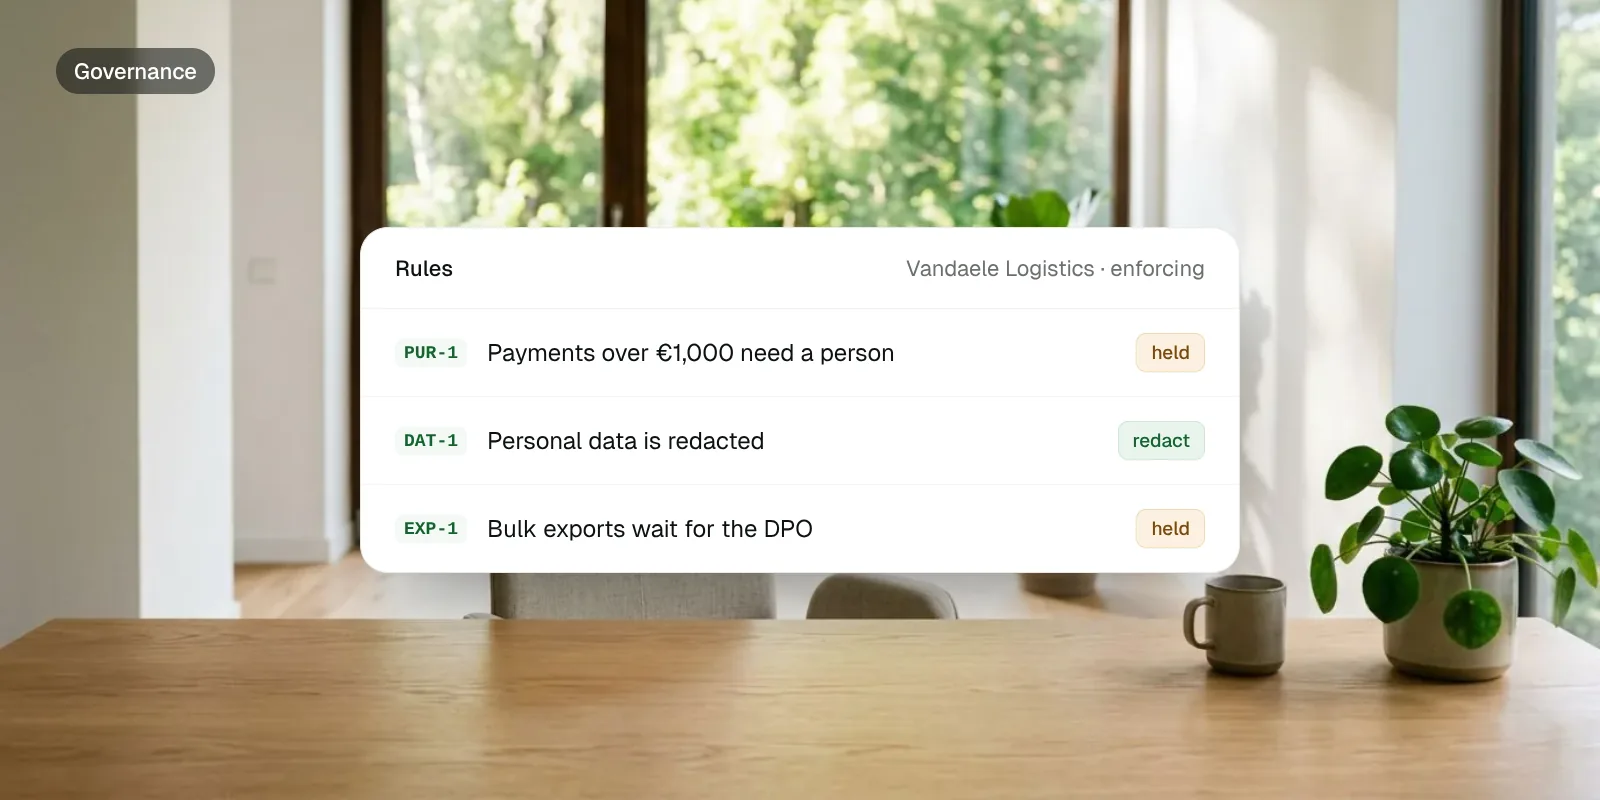
The Governance Gap: Why AI Agent Security Requires a New Category
AI agents are deploying faster than governance can keep up. Here's what needs to change.No posts match. Try another word or topic, or .
Start free. Watch your agents first.
Connect one agent and see every call TapPass would have held, stopped or routed elsewhere. Nothing is blocked while you learn.
✓ Free for one person✓ No credit cardBacked by 
 ✓ EU hosted✓ Built in Belgium✓ Your own model keys✓ Encrypted at rest and in transit✓ DPA on request